
Contents
iOS 27.2.1 Now Available. The Update Fixes 9 Security Vulnerabilities
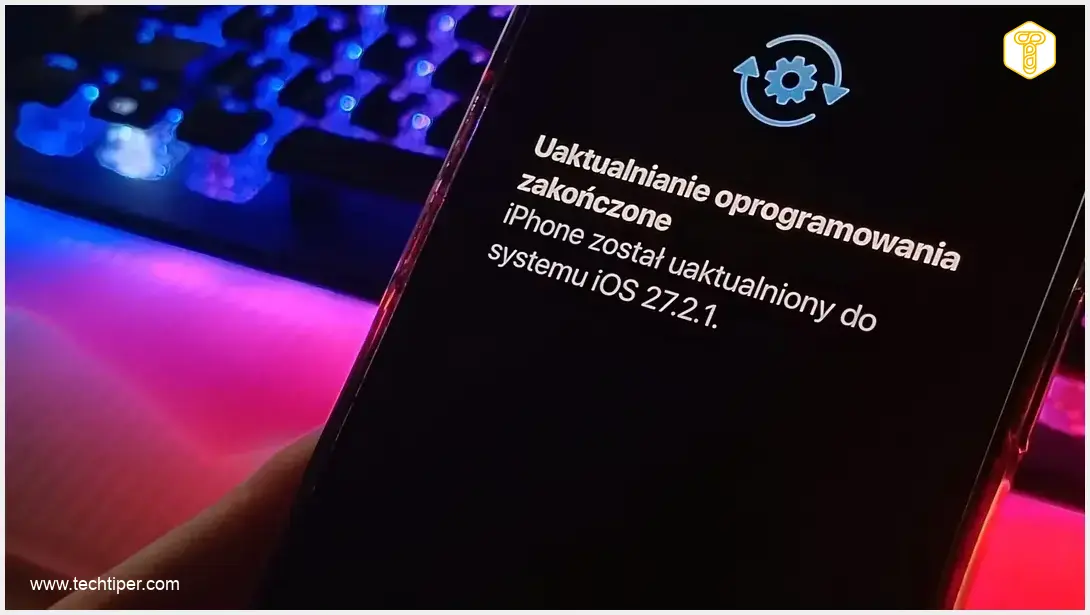
Apple has begun rolling out iOS 27.2.1, iPadOS 27.2.1, and macOS 27.2.1 globally for its devices. This critical update includes essential bug fixes and security enhancements, addressing several vulnerabilities related to Bluetooth, AirPlay, Messages, and applications’ access to user data. Users are strongly encouraged to update their devices without delay to ensure continued security and optimal performance.
Key Security Fixes in Apple’s Latest Updates
The iOS 27.2.1 security documentation details fixes for nine distinct vulnerabilities across seven system components. These patches specifically target issues within the Messages app, AirPlay, Bluetooth, and App Intents, reinforcing the security posture of your Apple devices. This widespread update highlights Apple’s commitment to user privacy and device integrity, crucial aspects in today’s digital landscape.
Critical Patches for iMessage
Two significant vulnerabilities within iMessage group conversations have been addressed in this update. The first, identified as CVE-2026-113961, involved an authorization flaw. This bug could potentially allow a remote attacker to join a group chat without authorization and intercept messages. Apple rectified this by strengthening permission verification, ensuring that only authorized participants can access private conversations.
The second iMessage vulnerability, CVE-2026-113960, concerned conversation history. It enabled individuals added to a group chat to access messages sent before their inclusion. With this update, Apple has closed this loophole, protecting the historical context of group communications from unauthorized viewing.
Enhancements for AirPlay and Bluetooth Security
Apple has also implemented crucial fixes for AirPlay and Bluetooth. For AirPlay, a vulnerability that allowed an attacker within Bluetooth range to bypass the pairing code attempt limit has been resolved. This could have potentially led to unauthorized access or control over AirPlay-enabled devices.
Further Bluetooth improvements, particularly within the CoreUtils component, address memory corruption issues. An attacker within Bluetooth range could have exploited these to corrupt process memory. Additionally, the update resolves problems that could allow a malicious device to pair without explicit user action, significantly bolstering device security against proximity-based attacks.
Protecting App Data and Brotli Library Fix
iOS 27.2.1 also mends an authorization error in App Intents, tagged as CVE-2026-113963. This flaw could have potentially granted applications access to sensitive user data without proper authorization. Apple’s solution involved enhancing state management within App Intents, thereby safeguarding user information. Furthermore, a vulnerability in the Brotli compression library has been patched. This issue could lead to memory corruption if specially crafted data were processed, demonstrating Apple’s vigilance in securing even underlying system components.
Who Can Download iOS 27.2.1 and How to Update?
According to Apple’s security bulletin, the iOS 27.2.1 update is available for iPhone 11 and newer models. To check if the update is ready for download and installation on your device, navigate to Settings, then General, and finally, Software Update. It is highly recommended to install this update promptly, especially given the privacy-related fixes for conversations and device pairing security.
While you might not notice any visible changes to your phone’s appearance or new features, the most significant improvements operate in the background. These changes are crucial for mitigating specific security threats, ensuring your device remains protected against known vulnerabilities.
Updates Extend to Other Apple Devices
The parallel iPadOS update, iPadOS 27.2.1, is available for a range of iPad models:
- iPad Pro 12.9″ (4th generation and newer)
- iPad Pro 11″ (2nd generation and newer)
- iPad Air (4th generation and newer)
- iPad (9th generation and newer)
- iPad mini (6th generation and newer)
Concurrently, updates have also been released for other Apple platforms, including macOS Golden Gate 27.2.1. These updates address similar vulnerabilities concerning Messages, AirPlay, and Bluetooth across Mac computers, ensuring a consistent level of security across Apple’s ecosystem.
Frequently Asked Questions (FAQ)
These updates primarily focus on critical security fixes and bug resolutions. They address nine vulnerabilities across various system components, including Messages, AirPlay, Bluetooth, and app data access, significantly enhancing the overall security and privacy of your Apple devices.
The update fixes vulnerabilities that could allow unauthorized access to iMessage group chats (CVE-2026-113961, CVE-2026-113960), bypass AirPlay pairing limits, facilitate malicious Bluetooth pairing, lead to memory corruption in Bluetooth and Brotli library, and allow unauthorized app access to sensitive user data via App Intents (CVE-2026-113963).
No, these updates are primarily focused on backend security enhancements and bug fixes. You should not expect any noticeable changes to your device’s interface or the introduction of new user-facing features. The improvements are all about strengthening your device’s security and privacy.
While updates are designed to improve performance and security, if you encounter any issues, try restarting your device first. If problems persist, check Apple’s official support pages for troubleshooting tips or contact Apple Support directly.
Source: TheTechOutlook, Apple, PCMag
Opening photo: Jolanta Szczepaniak
About Post Author
